
ZoTrus, Cryptographic Application
Automation Provider
Cryptography for Trust. Automation for Security. AI for Productivity.
Certificates Exist. But It Still Falls Short Without Automation
Digital certificates establish trusted identities and enable encryption and digital signatures. Certificate authorities issue certificates, while applications use them. Yet these two sides have traditionally operated separately. Obtaining a certificate does not automatically install it, renew it, configure an application, or ensure that cryptographic operations are performed when needed. Users and IT teams are often left to connect the pieces manually. The result is a persistent gap between certificate infrastructure and practical cryptographic applications.
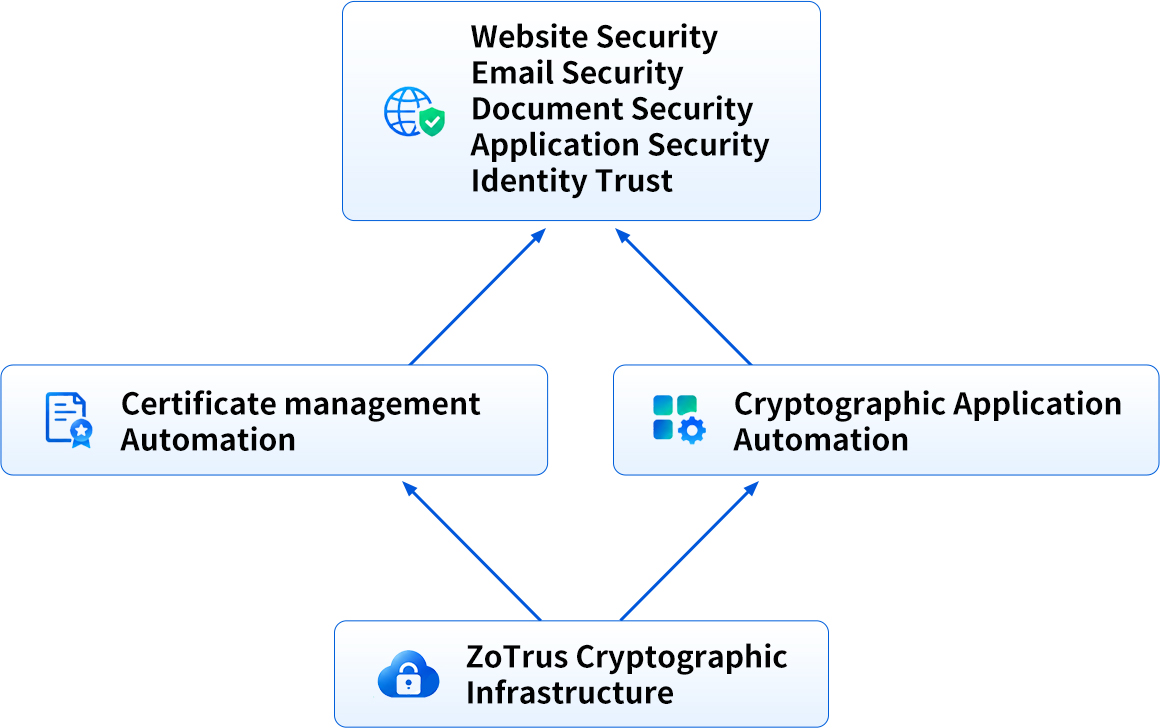
ZoTrus addresses this gap by connecting certificate management automation with cryptographic application automation. Achieve automated protection for website security, email security, document security, application security, and identity trust through certificate automation and application automation, making cryptography easier to deploy, manage, and use.
Certificates Establish Trust. Automation Makes Trust Work.
- Certificate management Automation Automate certificate enrollment, deployment, renewal, and management.
- Cryptographic Application Automation Integrate digital signatures, encryption, decryption, and validation into real application workflows.
- Unified Cryptographic Infrastructure Connect certificate authorities, trust services, applications, and security systems through a common infrastructure.
Zero Trust Is More Than Access Control.
Zero Trust is often discussed primarily in terms of identity authentication and access control. A broader understanding also addresses devices, network traffic, applications, workloads, and data. The U.S. Federal Zero Trust Strategy provides an important reference for this broader security architecture, including traffic encryption and automation. Building on this wider security perspective, ZoTrus has developed its own Three Concepts and Five Principles to explain how zero trust can be translated into practical, cryptography-based security.
Three Concepts of ZoTrus
Never Trust.Always Verify.Always Encrypt.
These concepts guide how trusted identities, digital certificates, cryptographic protection, and application workflows work together.
Five Principles for Cryptographic Security
- Website Security: Automatically protect website connections with authenticated, encrypted HTTPS.
- Email Security: Automatically use trusted identities, digital signatures, and encryption to protect email communications.
- Document Security: Automatically establish document authenticity, signer identity, integrity, and confidentiality through digital signatures and encryption.
- Application Security: Automatically integrate cryptographic protection into applications CI/CD workflows.
- Identity Trust: Use digital certificates and appropriate identity validation to establish verifiable identities for people and organizations.
Digital certificates, public key infrastructure (PKI), digital signatures, and encryption provide essential technical foundations for implementing these principles. Cryptographic application automation helps bring them to practical use. Read more: Read In-Depth Interpretation of the U.S. Federal Zero Trust Strategy [1] [2] [3].
Explore the Three Concepts and Five Principles of ZoTrusOne Foundation. Multiple Applications. Automated Cryptographic Application for Security.
ZoTrus provides a unified cloud cryptographic infrastructure that connects certificate authorities, trusted identities, certificate lifecycle management, and cryptographic operations. Instead of treating every application as an isolated security problem, ZoTrus provides a shared foundation for automating cryptographic capabilities across different services and deployment environments.
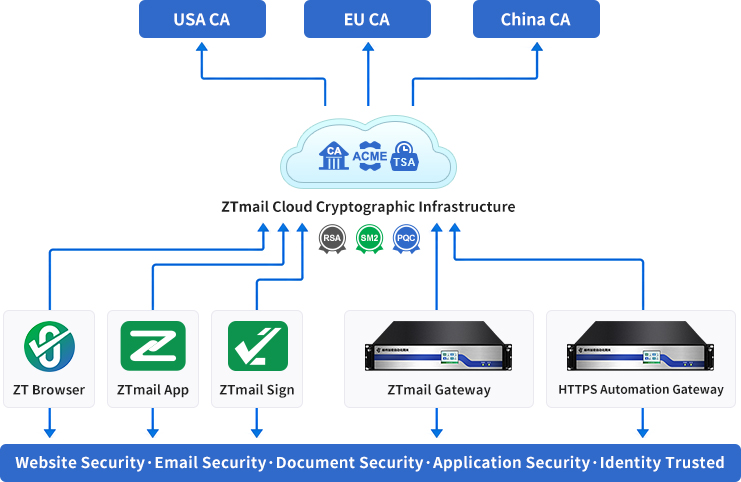
- Multi-CA Connectivity Connect with multiple certificate authorities and trust services, enabling certificate selection and management according to certificate type, validation requirements, trust policies, and application needs.
- Automated Certificate Lifecycle Management Automate certificate enrollment, issuance workflows, deployment, renewal, and management through appropriate protocols and integrations, reducing manual intervention and operational overhead.
- Cryptographic Application Automation Connect certificates and cryptographic operations to the applications that need them, enabling digital signing, validation, encryption, and decryption within practical workflows.
- Flexible Deployment Use application-based services for individuals and small businesses, or centralized gateways and integrations for large organizations. Both approaches build on the same underlying philosophy of automated cryptographic security.
One Foundation. Multiple Applications. Automated Cryptographic Application for Security.
ZoTrus provides a unified cloud cryptographic infrastructure that connects certificate authorities, trusted identities, certificate lifecycle management, and cryptographic operations. Instead of treating every application as an isolated security problem, ZoTrus provides a shared foundation for automating cryptographic capabilities across different services and deployment environments.
Signature · Validation · Encryption · Decryption · Trusted Digital Identity
Certificate Lifecycle Automation
Automate certificate enrollment, deployment, renewal, and management using suitable protocols and integrations, including ACME where applicable.
Trusted Identity Automation
Connect certificate-based identities with email, websites, documents, applications, and organizational workflows to make identity verification more practical and consistent.Digital Signature and Validation
Integrate certificate-based signing and signature validation into application workflows to help establish authenticity, signer identity, and document or message integrity.Encryption and Decryption
Make cryptographic protection part of normal application operations rather than a separate task that users must manage manually.Multi-Algorithm Support
Support different cryptographic algorithms and deployment approaches, helping applications meet interoperability, compatibility, and compliance security requirements without relying on a single algorithmic path.Complete Cryptographic Capabilities
Let existing systems and security devices focus on their main functions, leaving cryptographic tasks to an automated cryptographic application gateway, so organizations can improve security without having to replace or upgrade their current systems and devices.More Cryptographic Choices. Greater Interoperability. A More Resilient Internet.
Global Internet security requires open standards, interoperable implementations, and diverse cryptographic technology choices. ZoTrus supports automated cryptographic applications using both dual-algorithm and multiple-algorithm approaches, helping customers select and deploy appropriate cryptographic technologies according to their actual application requirements. RSA and SM2 are both internationally standardized cryptographic algorithms, although SM2 still has a different level of adoption across the global application ecosystem. ZoTrus supports certificate automation and cryptographic application automation for both RSA and SM2, making different cryptographic technologies easier to deploy in real-world business applications and giving users more choices, including hybrid post-quantum cryptographic algorithms.
RSA · ECC · SM2 · X25519MLKEM768 · SM2MLKEM768 · MLDSA · MLKEM
Website Security
- Supports dual-algorithm SSL certificate automation
- Supports multi-algorithm key encapsulation
- Supports traditional cryptography and hybrid PQC
- ZT Browser supports multiple cryptographic algorithms
- ZoTrus HTTPS Automation Gateway supports multiple cryptographic algorithms
- Supports automatic switching among multiple CAs
Email Security
- Supports dual-algorithm S/MIME certificate automation
- Supports dual-algorithm digital signatures and encryption
- Will support PQC algorithms
- ZTmail App supports multiple cryptographic algorithms
- ZoTrus S/MIME Automation Gateway supports multiple cryptographic algorithms
- Supports automatic switching among multiple CAs
Document Security
- Supports dual-algorithm document certificate automation
- Supports dual-algorithm digital signatures and encryption
- Will support PQC algorithms
- ZTmail Sign supports multiple cryptographic algorithms
- ZoTrus Document Cryptographic Application Automation Gateway supports multiple cryptographic algorithms
- Supports automatic switching among multiple Cas
- Supports both local signing and cloud-based HASH signing
Application Security
- Supports dual-algorithm code signing certificate automation
- Supports dual-algorithm code signing
- ZTmail Sign supports multiple cryptographic algorithms
- Supports automatic switching among multiple Cas
- Supports both local signing and cloud-based HASH signing
- ZoTrus Code Signing Automation System supports multiple cryptographic algorithms
Identity Trust
- Supports dual-algorithm identity certificate automation
- Provides unified identity management and unified identity authentication based on digital certificates
- Supports automatic switching among multiple Cas
- A single identity validation can be reused to apply for the corresponding certificates for website trusted identities, email trusted identities, document trusted identities, and code trusted identities
Algorithm Diversity as a Design Principle. Cryptographic Agility as an Implementation Approach. Automation as the Way to Bring It into Practice.
ZoTrus does not assume that any single cryptographic technology will necessarily be the only choice capable of meeting all future security requirements. Supporting multiple technological paths provides greater flexibility for interoperability, compliance, deployment, evaluation, and future evolution as cryptographic technologies continue to develop. ZoTrus does not promote one algorithm for every application scenario. Instead, ZoTrus help make different cryptographic technologies easier to deploy, manage, and interoperate in real-world applications.One Cryptographic Foundation. Six Security Domains.
ZoTrus applies a shared cryptographic foundation and automation philosophy to six connected areas of security. Each domain addresses a different application need while benefiting from trusted identities, certificate management automation, and automated cryptographic operations.
Website Security
Automate TLS/SSL certificate management and website cryptographic configuration. Support appropriate certificate and TLS configurations to reduce manual work and improve operational consistency.
For individuals and small businesses: Automated certificate subscription services and ACME client tools.
For large organizations: Centralized HTTPS Automation Gateway and integrations for website fleets and enterprise infrastructure.
Email Security
Bring certificate-based identity, digital signatures, and encryption into everyday email workflows. Automate S/MIME certificate management and cryptographic operations to help users protect messages without turning security into a separate technical process.
For individuals and small businesses: ZTmail App and related email security services.
For large organizations: Centralized S/MIME Automation Gateway and integrations with existing email infrastructure.
Chat Security
Apply trusted identity and cryptographic protection to chat and messaging workflows built around email infrastructure and related integrations. Help users establish who they are communicating with and encrypt messages where supported.
For individuals and small businesses: ZTmail App and its integrated communication experience.
For large organizations: Enterprise Instant Messaging Encryption Gateway and system integrations.
Document Security
Integrate certificate-based digital signing, signature validation, and document encryption into document workflows, from email attachments to local files and enterprise systems. Support different trust models and signing scenarios while keeping cryptographic operations connected to the workflows in which documents are created, exchanged, and used.
For individuals and small businesses: ZTmail App and related document security services.
For large organizations: Centralized Document Cryptographic Application Automation Gateway and business-system integrations.
Application Security
Bring certificate lifecycle automation and cryptographic operations into applications, APIs, and business systems. Help developers and IT teams integrate trusted identities and cryptographic protection into existing CI/CD workflows.
For individuals and small businesses: ZTmail App and related document security services.
For large organizations: Centralized Code Signing Automation System and automated application security workflow integrations.
Identity Trust
Use appropriate certificate profiles and identity validation processes to establish verifiable identities for individuals, employees, and organizations. Connect identity assurance with actual cryptographic operations so that trusted identity becomes useful in email, websites, documents, and applications.
Algorithm Diversity as a Design Principle. Cryptographic Agility as an Implementation Approach. Automation as the Way to Bring It into Practice.
ZoTrus does not assume that any single cryptographic technology will necessarily be the only choice capable of meeting all future security requirements. Supporting multiple technological paths provides greater flexibility for interoperability, compliance, deployment, evaluation, and future evolution as cryptographic technologies continue to develop. ZoTrus does not promote one algorithm for every application scenario. Instead, ZoTrus help make different cryptographic technologies easier to deploy, manage, and interoperate in real-world applications.Different Deployment Models. One Automation Philosophy.
Cryptographic security should not require every user or organization to build and maintain a complex PKI environment. ZoTrus provides different ways to use the same underlying cryptographic capabilities, according to operational scale, integration requirements, and security policies.
Apps and Cloud Services
For individuals and small businesses, app-based services and cloud infrastructure simplify certificate management and cryptographic operations without requiring a dedicated enterprise gateway.
- Download and install App
- Integrated user workflows
- Automated certificate lifecycle management and operations
- Practical digital signatures and encryption
- Access to appropriate trusted identity options
Enterprise Gateways and Integrations
For large organizations, centralized gateways and integrations help automate cryptographic operations across existing security infrastructure, business systems, websites, email environments, and document workflows.
- Centralized certificate automation and cryptographic management
- Automated HTTPS and email security workflows
- Document and application cryptographic integrations
- Support for organizational policies and operational requirements
- Integration with existing systems rather than wholesale replacement
App for Individuals and Small Businesses. Gateway for Enterprise Organizations.
Download ZTmail AppExplore ZTmail GatewayDownload ZT BrowserExplore ZoTrus HTTPS Automation GatewayBuilding Four Ecosystems Around Cryptographic Application Automation
Over more than five years of research and development, ZoTrus has built three cryptographic application ecosystems and is now developing a fourth: the Post-Quantum Cryptographic Application Ecosystem. Built on unified cryptographic infrastructure and cryptographic application automation technologies, these four ecosystems address different cryptographic technologies and application requirements, covering SM2 SSL certificate transparency, automatic certificate management, email-based cryptographic applications, and post-quantum cryptographic applications. Together, they provide crypto-agile automated application solutions for website security, email security, document security, code signing, trusted identity, and other application scenarios. By default, all products and solutions support dual-algorithm digital certificate solutions based on SM2 and RSA/ECC, providing flexibility and compliance across different cryptographic environments and application requirements.
Certificate Transparency Ecosystem
ZoTrus pioneered the world's first SM2 Certificate Transparency (SM2 CT) ecosystem and continues to operate the world's only operational SM2 CT ecosystem today. Built on international Certificate Transparency standards and implemented with SM2 cryptography, it brings transparency, auditability, and verifiable trust to SM2 SSL certificates and RSA/ECC SSL certificate.
- SM2 Certificate Transparency System — A deployable CT system
- SM2 CT Log Operation — Three operational SM2 CT log services operated by ZoTrus
- ZT Browser Supporting SM2 Certificate Transparency
- ZoTrus CA System Supporting SM2 Certificate Transparency
- SM2 SSL Certificates Supporting Certificate Transparency
SSL Certificate and HTTPS Automation Ecosystem
Referring to the international SSL certificate automation management ecosystem, provide dual-algorithm SSL certificate automated request, issuance, deployment, renewal, and management capabilities. It connects CA services, ACME automation, client software, gateways, and cloud services to make dual-algorithm SSL certificate management and HTTPS encryption more efficient and reliable.
- ZoTrus ACME Service System
- ZoTrus CA System for Issuing SM2/RSA SSL Certificates
- ZT Browser Supporting SM2/RSA SSL Certificates
- SM2cerBot — SM2 ACME Client, for dual-algorithm SSL certificates
- ZoTrus SSL Certificate Automation Subscription Service
- ZoTrus HTTPS Automation Gateway
- ZoTrus HTTPS Automation Cloud Service
ZTmail.AI Cryptographic Application Automation Ecosystem
Built on email infrastructure, this ecosystem integrates trusted identity, certificate lifecycle management, and cryptographic application automation into email, chat, and document workflows. It extends automated cryptographic applications across these three domains, providing integrated security for digital communications and document workflows.
- ZTmail.AI ACME Service System
- ZTmail CA System for Issuing SM2/RSA S/MIME and Document Certificates
- ZTmail App
- ZTmail Email Cryptographic Application Service
- ZTmail Chat Cryptographic Application Service
- ZTmail Sign Cryptographic Application Service
- ZTmail Cryptographic Application Automation Gateway
Post-Quantum Cryptographic Application Ecosystem
Designed to address the development and migration requirements of post-quantum cryptography, this ecosystem supports multiple cryptographic algorithms and hybrid cryptographic approaches. It aims to bring post-quantum cryptographic capabilities into websites, email, documents, and other application scenarios, providing automation support for future cryptographic migration and long-term security evolution.
- ZT Browser Supporting Dual-Hybrid PQC
- ZoTrus HTTPS Automation Gateway Supporting Dual-Hybrid PQC
- PQC Algorithm Root Certificates and CA System — In Development
- PQC SSL/S/MIME/Document Certificates — In Development
- ZT Browser Supporting PQC SSL Certificates — In Development
- ZoTrus HTTPS Automation Gateway Supporting PQC SSL Certificates — In Development
- PQC Algorithm Certificate Transparency Log System — In Development
- PQC Algorithm Certificate ACME Service System — In Development
- MTC Certificate Research — Ongoing
Four Ecosystem Products · Multiple Cryptographic Technologies · Crypto-Agile Automation Across Application Domains
From SM2 certificate transparency and automatic certificate management to email-based cryptographic applications and post-quantum cryptography, ZoTrus continues to bring cryptographic technologies from standards and infrastructure into real-world business applications.
One Cryptographic Foundation. Connected Ecosystems. Automated Cryptographic Applications.
Cryptographic application automation requires not only products and technologies, but also open standards. These are essential foundations for interoperability and scalable cryptographic automation. ZoTrus connects Certificate Authorities, email service providers, application providers, and web security systems through shared cryptographic infrastructure and automation concepts. Our ecosystem initiatives cover Website Security, Email Security, Chat Security, Document Security, Application Security, and Identity Trust. Different fields have their own service providers, protocols, and deployment requirements, but they can all benefit from a unified foundation for certificate management and cryptographic application automation.
ZTmail.AI, One-Stop Cryptographic Application Automation Platform for Email, Chat, and Documents
- Core international standards: S/MIME, CMS, RFC 8823, RFC 8555 etc.
- Supported algorithms: RSA, ECC, SM2, MLDSA, MLKEM etc.
- Applicable draft Chinese commercial cryptography standards: Automatic Certificate Management Protocol (led by ZoTrus)
- Certificate industry standards: CA/Browser Forum S/MIME Certificate Baseline Requirements
- Client compatibility: ZTmail App, Outlook, Thunderbird, Apple Mail, Adobe Reader
- Cloud Services: ZTmail ACME Service (dual-algorithm S/MIME certificates), ZoTrus Timestamping Service
- Multi-CA support: ZoTrus CA, Sectigo, SSL.com, BJCA, CFCA, GZCA, DFCA etc.
- IMAP/SMTP support: for all email services with two deployment options: App and Gateway
Website Security Solutions: One ACME Standard, Three HTTPS Deployment Methods
- Core international standards: TLS, HTTPS, RFC 8555, RFC 6962 etc.
- Supported algorithms: RSA, ECC, SM2, X25519MLKEM768, SM2MLKEM768, MLDSA, MLKEM etc.
- Applicable draft Chinese commercial cryptography standards: Certificate Transparency Framework and Automatic Certificate Management Protocol (led by ZoTrus)
- Certificate industry standards: CA/Browser Forum TLS Certificate Baseline Requirements
- Browser compatibility: ZT Browser, Google Chrome, Microsoft Edge, Apple Safari, and Firefox
- Cloud Services: ZoTrus ACME Service (dual-algorithm SSL certificates)
- Multi-CA support: ZoTrus CA, Sectigo, SSL.com, SHECA, CFCA, GZCA, DFCA etc.
- Three HTTPS deployment methods: ACME Gateway, ACME Cloud Service, and ACME Client
Making Standards Interoperable. Making Automation Bring Standards into Practice. Connecting Global Ecosystems. Collaborating Across the Industry to Build a More Secure Digital Future!
Explore the Global Cryptographic Application EcosystemOne Cryptographic Foundation. Connected Ecosystems. Automated Cryptographic Applications.
Cryptographic application automation requires not only products and technologies, but also open standards. These are essential foundations for interoperability and scalable cryptographic automation. ZoTrus connects Certificate Authorities, email service providers, application providers, and web security systems through shared cryptographic infrastructure and automation concepts. Our ecosystem initiatives cover Website Security, Email Security, Chat Security, Document Security, Application Security, and Identity Trust. Different fields have their own service providers, protocols, and deployment requirements, but they can all benefit from a unified foundation for certificate management and cryptographic application automation.
SM2MLKEM768 and TLS Code Point 4590
- Advancing the practical implementation of SM2MLKEM768 by combining the elliptic-curve cryptographic technology based on SM2 with the post-quantum key encapsulation mechanism ML-KEM-768.
- Successfully applied to IANA for the allocation of TLS Supported Groups code point 4590 to SM2MLKEM768, giving this scheme a corresponding identifier in the Internet protocol ecosystem. This is a concrete example of cryptographic diversity extending into TLS and post-quantum hybrid key exchange.
ZT Browser and HTTPS Automation Gateway Support Hybrid PQC Algorithms
- Supports the hybrid PQC algorithm X25519MLKEM768.
- Supports the SM2-based hybrid PQC algorithm SM2MLKEM768.
- ZT Browser introduces a green Q indicator in its address bar to make quantum-safe visible to users.
- ZoTrus HTTPS Automation Gateway enables a coordinated transition to cryptography compliance and PQC migration through a single deployment.
Cryptographic Diversity Is a Practical Strategy for Strengthening Long-Term Security Resilience
- Supporting multiple hybrid PQC algorithm paths preserves the value of having multiple cryptographic technology choices, rather than assuming that any single solution can meet all future requirements.
- Supporting multiple alternatives does not mean relaxing rigorous cryptographic analysis, security testing, and continuous evaluation. It means having more choices as cryptographic technologies and the ecosystem continue to evolve.
Connecting Trust, Cryptography, and Applications
ZoTrus focuses on the part of digital security that is often left between infrastructure and applications: making cryptographic capabilities work automatically in practice.
A Unified Cryptographic Foundation
Connect certificate authorities, trust services, certificate lifecycle operations, and application-level cryptographic capabilities.
Zero Trust Principles
Apply trusted identity, verification, and encryption through practical cryptographic mechanisms across different application domains.
Certificate Management Automation
Reduce manual certificate operations and help keep certificates appropriately deployed and managed throughout their lifecycle.
Cryptographic Application Automation
Bring digital signatures, validation, encryption, and decryption into real application workflows.
Dual-Algorithm and Multi-Algorithm Support
Support RSA, SM2, and hybrid post-quantum key exchange, to provide more choices for compatibility, deployment, and future evolution.
Flexible Deployment
Serve individuals and small businesses through applications and cloud services, and large organizations through centralized gateways and system integrations.
Open Standards and Ecosystem Collaboration
Connect international protocols, Chinese commercial cryptography standards, certificate authorities, and application providers.
Don't Replace. Complete.
ZoTrus helps complete the connection between trusted identities, digital certificates, cryptographic technologies, and the applications that depend on them.
One Trust Program. Two Application Ecosystems.
ZoTrus Trusted Root Program establishes a unified digital trust foundation, providing certificate root trust for secure web browsing, email, and document communication. The program encompasses two cryptographic application ecosystems; each designed for different digital trust scenarios with its corresponding certificate root trust system.

ZT Browser — TLS / SSL Certificate Roots Trust
Provides SSL certificate root trust for websites and HTTPS connections, helping users verify website identities and establish a trusted web browsing environment. This includes trust lists for RSA/ECC and SM2 root certificates, as well as trust lists for RSA/ECC and SM2 Certificate Transparency (CT) log systems.
ZTmail App — Email & Document Certificate Roots Trust
Provides certificate root trust for email and documents, helping users verify email identities and validate digital signatures on documents, thereby establishing a trusted digital communication and document environment. This includes trust lists for RSA/ECC and SM2 root certificates, as well as trust lists for RSA/ECC and SM2 timestamping services.
One unified trust program. Two specialized application ecosystems. A shared foundation of digital trust across websites, email, and documents.
Learn MoreAutomate Certificate Management. Automate Cryptography in Applications.
Whether securing websites, email, chat, documents, applications, or digital identities, ZoTrus helps connect certificate infrastructure with the cryptographic operations your applications need. Automate certificate management. Integrate cryptographic operations. Support diverse algorithms. Build security into everyday workflows.