Free, Clean, Ad-Free
Cryptographic Agility. Visible Security. Digital Trust.
RSA ▪ ECC ▪ SM2 ▪ PQC
A familiar browsing experience is not the whole story. As cryptographic standards evolve and online threats become more sophisticated, users need more than an encrypted connection: they need the ability to understand the security technologies in use and assess who is behind the websites and documents they access. ZT Browser builds on Chromium and adds focused capabilities for RSA/ECC/SM2 cryptography, post-quantum cryptography readiness, visible website identity, Certificate Transparency, and PDF document signature verification. It is designed to make important security information more accessible without requiring users to become cryptography experts.
Across RSA, ECC, and SM2, and two Hybrid PQC.
For HTTPS connection and website security properties.
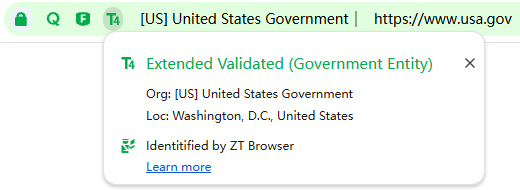
Display Website identity based on SSL certificate type.
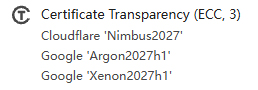
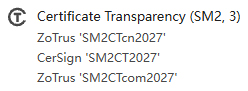
Display Certificate Transparency information details.
With digital signature verification and trusted signer identity display.
Cryptographic technologies continue to evolve. A browser should be prepared to work with established algorithms today while supporting the transition to new cryptographic approaches. ZT Browser is designed around cryptographic agility: the ability to adopt, support, and transition between cryptographic algorithms as standards, infrastructure, and security requirements evolve. This contributes to cryptographic resilience, the ability to maintain security and service continuity through cryptographic change.
ZT Browser supports cryptographic algorithm families including RSA, ECC, and SM2. And two hybrid post-quantum key exchange: X25519MLKEM768, SM2MLKEM768, that combine classical and post-quantum cryptographic components.
An HTTPS connection helps protect data in transit, but encryption alone does not tell users everything about the identity of a website. The familiar security indicator should not be mistaken for proof that a site belongs to a particular bank, company, or government organization. ZT Browser adds visible indicators to help users understand more security properties of the current website and HTTPS connection.
Indicates that the current connection uses HTTPS encryption.
Indicates that the current HTTPS connection uses a supported hybrid PQC.
Indicates that the current HTTPS connection uses SM2 algorithm.
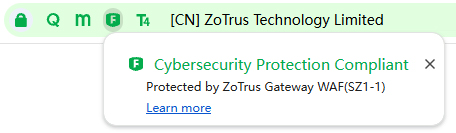
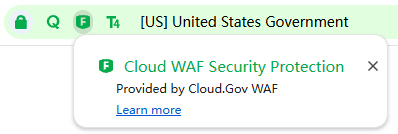
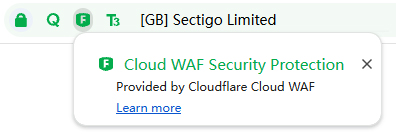
Indicates that the website has been identified as using WAF protection.
A website can use HTTPS without proving that it belongs to the organization a visitor expects. ZT Browser helps make certificate-based website identity information more visible by recognizing certificate types from the relevant certificate Object Identifiers (OIDs).
These website identity types are identified in accordance with the CA/Browser Forum SSL Baseline Requirements. ZT Browser uses the relevant OIDs to identify the certificate type and presents it through the T1–T4 visual indicators. T1–T4 are ZT Browser visual identity indicators; they are not level names independently defined by the CA/Browser Forum.
Visible identity information can help users distinguish domain-validated websites from certificates that provide individual, organization, or extended validation information. It can support more informed decisions when visiting websites that claim to represent banks, businesses, or public institutions.
DV SSL certificates make HTTPS deployment simple and efficient through automation. They provide encrypted connections and validate domain control. However, DV certificates do not validate the real-world identity of the individuals or organizations operating a website. Users cannot determine who is behind a website based on a DV certificate alone.
With the ZoTrus Website Trusted Identity Validation Service, both individuals and organizations can apply for trusted website identity validation. Websites can retain their DV SSL certificates while obtaining independent identity validation. Once validated and recognized by ZT Browser, the Browser can display the corresponding identity validated level, validated individual or organization name, and associated address bar appearance. This approach preserves the convenience of automated DV certificate deployment while filling the gap in website identity validation.

Certificate Transparency (CT) helps make the issuance of publicly trusted certificates more observable. ZT Browser brings CT information together in one interface, helping users inspect certificate transparency details rather than seeing only that CT is present.
By displaying CT Log names and operators, ZT Browser makes certificate transparency information easier to inspect. ECC CT and SM2 CT support helps bring transparency information from both cryptographic ecosystems into the same browsing experience.


Web Application Firewalls (WAFs) help protect websites by inspecting web traffic and identifying or filtering potentially harmful requests. ZT Browser can visibly identify a website that has been recognized as using WAF protection through the F indicator. The indicator gives users an additional piece of security context while browsing. It is an indication of identified WAF protection, not a guarantee that a website is free from vulnerabilities or attacks.


When ZT Browser displays “Protected by ZoTrus Gateway WAF (SZ1-1)” (see above first screenshot), it indicates that the website is fronted by a ZoTrus HTTPS Automation Gateway, with protection provided by its built-in WAF. The identifier in parentheses, such as “SZ1-1”, indicates the gateway's deployment location. This makes gateway protection visible and let ZT Browser users see the security behind the website.
PDF files are widely used to exchange business documents, statements, notices, contracts, and official information. A document can display a company name, logo, or image of a seal, but those visual elements alone do not establish who issued the document or whether its content has been altered. ZT Browser includes a built-in PDF reader that brings digital signature verification and trusted signer identity information into the document-reading experience. Its security presentation is designed to align with the identity and signature experience in ZTmail Sign.
View signature status and verification results, including relevant trust information and document modification status.
Identify whether the document is encrypted by certificate and decryption.
View trusted timestamp information associated with the document digital signature.
Inspect long-term validation information where supported by the document and validation data.
Display the signer’s certificate identity validation type using the applicable identity indicators.
Recognize SM2 digital signatures and support verification of SM2-signed PDF and OFD documents, and SM4 decryption.
For document signer identity, ZT Browser identifies the relevant certificate validation types through the multipurpose certificate Object Identifiers (OIDs) defined by the CA/Browser Forum S/MIME Baseline Requirements (S/MIME BR). The T1–T4 visual indicators in this document-signing context represent MV, IV, OV, and SV respectively.
“No digital signature, Identity is unknown. Be careful!” This warning means that the publisher’s identity cannot be verified through a digital signature in the document. It does not mean that every unsigned document is fraudulent. Users should exercise appropriate caution, especially when a document claims to come from a bank, company, or government institution. Digital signature verification helps users assess signer identity and document integrity. It can make attempts to impersonate trusted organizations easier to detect.
ZT Browser participates in the ZoTrus Trusted Root Program for SSL certificate trust. The program supports trusted certificate ecosystems for both RSA/ECC and SM2 ecosystem, and includes the intranet SSL certificate.

The broader ZoTrus Trusted Root Certification Program also serves the ZTmail App ecosystem for email and document certificate trust, including RSA/ECC and SM2 root certificates and trusted timestamping services. ZT Browser focuses on the SSL certificate and website trust components relevant to browsing, the built-in PDF reader uses the document certificate trust and timestamping trust.